The Difference Between Software Updates and Upgrades explains why small fixes and big releases matter differently. When an organization delays a security patch by two weeks, it risks a breach: when it postpones a platform upgrade by two years, it may lose vendor support. This guide gives a clear, practical way to tell updates from upgrades, so teams know when to act, what to back up, and how to weigh risk, cost, and user impact.
Key Takeaways
- Software updates are frequent, incremental fixes that address security vulnerabilities and minor bugs with minimal user impact.
- Software upgrades are less frequent, larger changes that add new features, alter interfaces, and often require detailed planning and user training.
- Timely installation of software updates reduces immediate security risks, while delaying upgrades can lead to loss of vendor support and increased maintenance costs.
- Updates typically involve low risk and cost, whereas upgrades carry higher costs, implementation risks, and necessitate rollback strategies.
- Effective software management involves automating updates for speed and prioritizing thorough testing and communication during upgrades to minimize disruptions.
- Distinguishing between software updates and upgrades helps organizations balance urgency, cost, risk, and user impact for better operational outcomes.
What Are Software Updates?
Fact first: software updates are incremental changes that fix problems, close security holes, or improve small behaviors. Updates typically address a narrow set of files and ship often, weekly, monthly, or on an emergency basis.
Updates are precise. A security patch might replace a single library file to stop a remote code execution bug. A bugfix can correct a crash when a user opens a specific report. They rarely change the user interface or database schema.
Practical example: a payroll app issues an update that resolves a rounding error affecting 2,847 payroll runs. The patch touches calculation routines only: employees see the same screens, and existing data stays intact. Because of that narrow scope, updates usually take minutes to install and can be tested with a small sample.
Operational note: teams treat updates as high-frequency, low-risk events that require a rapid rollback plan. They prioritize updates by impact: security > functional correctness > cosmetic. In many organizations, updates are automated: unattended patching for widely used components can close vulnerabilities within days.
Common follow-up: how to test them? A quick smoke test on staging that runs the vulnerable scenario and validates logs is often enough. For critical systems, a canary rollout to 5–10% of servers is a prudent compromise between speed and safety.
What Are Software Upgrades?
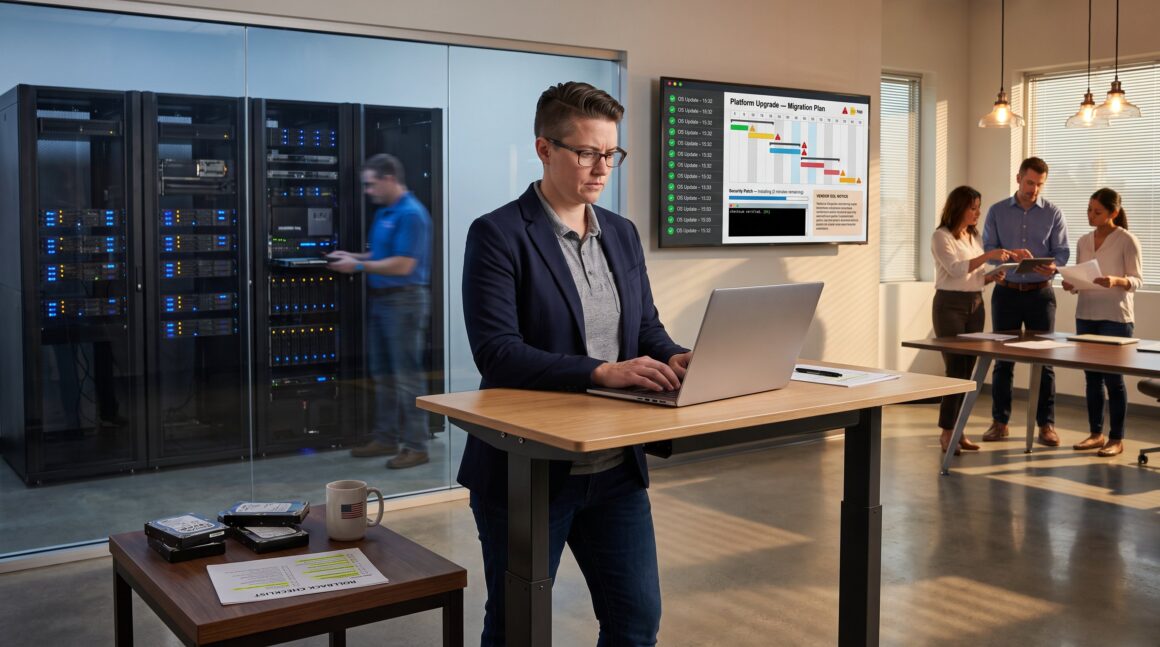
Answer up front: upgrades are larger releases that add functionality, change interfaces, or alter underlying platforms. They often require planning, compatibility checks, and longer downtime windows.
Upgrades shift the baseline. For example, moving an ERP from version 9 to version 11 can introduce new modules, change database schemas, and require retraining for 120 users. An upgrade may also drop support for legacy APIs that 37 internal scripts rely on. This connects with the site’s software guide, which covers related ground in more detail.
Timing and cadence: upgrades are less frequent, yearly or multi-year. Vendors announce end-of-life dates that force upgrades: delaying them risks losing security support and compliance certification.
Cost profile: upgrades cost more in testing, migration, and training. A mid-sized company reported the upgrade costed $78,400 for licensing, consulting, and two weeks of staff time, but it eliminated a manual reconciliation step that saved three hours per week across the finance team.
Human factor: upgrades change user behavior. Successful upgrades include staged training, clear release notes, and a rollback or compatibility mode when possible. Without that, productivity dips or users adopt shadow IT workarounds.
Key Differences: Purpose, Frequency, Risk, Cost, And User Impact
Straight answer: updates fix and secure: upgrades expand and evolve. Frequency, risk, cost, and user impact distinguish them clearly.
Purpose: updates address immediate defects and threats. Upgrades deliver new capabilities and longer-term architectural changes.
Frequency: updates appear frequently (days to months): upgrades are periodic (months to years).
Risk: updates carry low scope risk but high urgency for security fixes. Upgrades carry higher implementation and compatibility risk and require more rollback planning.
Cost: updates are low cost per event: combined they still consume resources. Upgrades are higher one-time costs for licensing, consulting, training, and migration.
User impact: updates are often invisible to end users: upgrades change workflows and require communication. A measurable example: after a UI upgrade, one company’s support tickets rose 210% during week one, then dropped below baseline after targeted training.
Operational trade-offs: organizations that auto-deploy updates reduce exposure but must maintain strong monitoring. Those that delay upgrades save short-term budget but face escalating maintenance costs and compliance risk.
Conclusion
Insight: treating updates and upgrades the same creates risk. Updates demand speed and automation: upgrades demand planning and human coordination. Teams that classify changes, test deliberately, and follow a simple checklist reduce outages and save money. The sensible rule: patch fast, upgrade deliberately.